About Shield & Sure
Experience from both sides of the table.
Security leadership shaped by running technology, auditing it, and protecting it, now focused on the businesses that need it most.
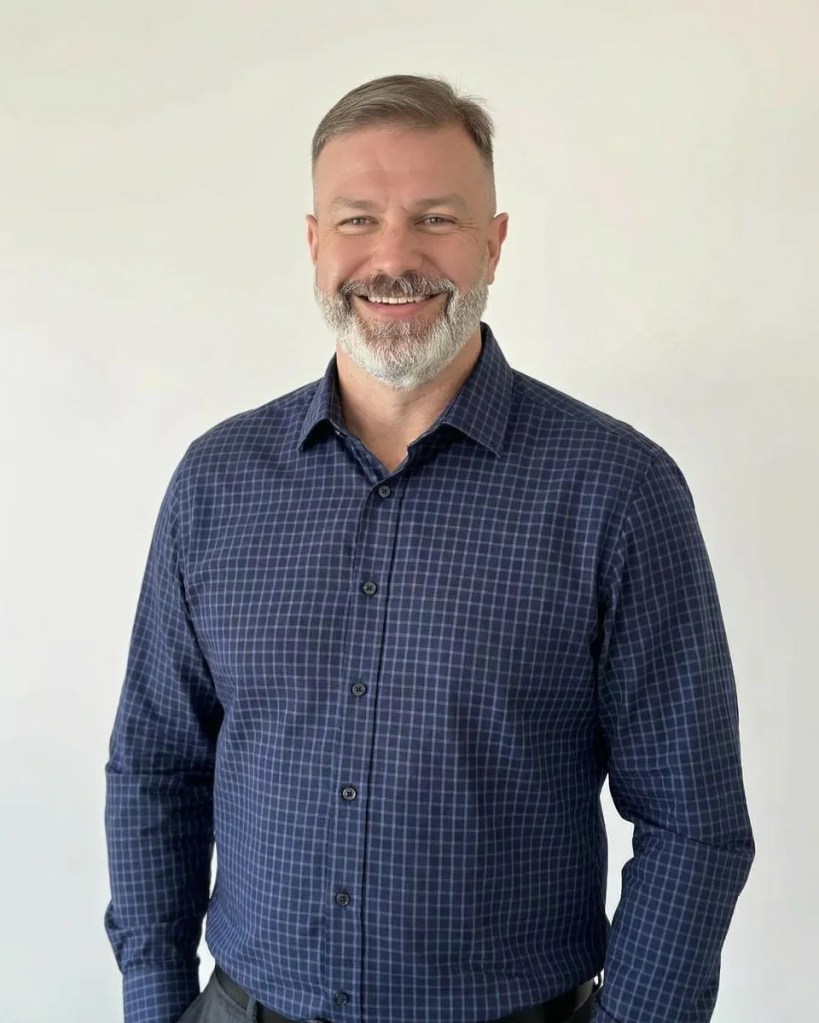
David Pahlman
Founder & Principal Consultant
LinkedIn · david@shieldandsure.com
Why Shield & Sure exists
Security leadership, sized for your business.
Small and midsize businesses face the same security expectations as large enterprises: customer security reviews, insurance questionnaires, regulatory obligations, and real attackers. What they usually lack is an experienced security leader to make sense of it all. Shield & Sure was built to close that gap with practical, right-sized guidance delivered in plain English.
I have spent more than 25 years on both sides of the security and compliance table. I have run technology as a healthcare CIO, evaluated other organizations’ controls as a professional IT auditor, and built and led security and compliance programs inside growing companies. I know what auditors and customers look for, and I know what it takes to meet those expectations with limited time, staff, and budget.
25+
Years in technology, security and compliance
9
Professional certifications
4
Audit frameworks assessed as an auditor
3
Seats at the table: CIO, auditor, security leader
Every seat at the table
The perspective you get comes from having done the job, checked the job, and been accountable for the result.
Healthcare CIO
Owned technology strategy, operations, and HIPAA compliance for a healthcare organization.
IT auditor
Assessed organizations against SOC 2, HIPAA, PCI DSS, and ISO 27001 from the auditor’s side.
Security & compliance leader
Built and ran security and compliance programs inside SaaS and healthcare data companies.
Engineering & services
Led security engineering and professional services, including public sector and critical infrastructure work.
Credentials
Independent, maintained certifications across security leadership, audit, risk, governance, and privacy.
CISSP
Certified Information Systems Security Professional
CISM
Certified Information Security Manager
CISA
Certified Information Systems Auditor
CRISC
Certified in Risk and Information Systems Control
CGEIT
Certified in the Governance of Enterprise IT
CDPSE
Certified Data Privacy Solutions Engineer
CEH
Certified Ethical Hacker
ECSA
EC-Council Certified Security Analyst
ISO 27001
Lead Auditor
How we work
Plain English
No jargon for its own sake and no fear tactics.
Proportionate
Recommendations sized to your risk, budget, and obligations.
Honest
No promises of perfect security or guaranteed audit results. Clear, accountable guidance.
Collaborative
We work alongside your IT team or managed service provider, not around them.
Let’s talk about your business
Start with a short, no-pressure conversation about where you stand and what matters most.

